
Dental offices across the United States handle some of the most sensitive personal data in healthcare. From patient records and X-rays to billing information, every byte of data is protected under the Health Insurance Portability and Accountability Act, better known as HIPAA.
Yet many dental practices underestimate how complex compliance has become. The U.S. Department of Health and Human Services (HHS) and its Office for Civil Rights (OCR) have increased enforcement over the last decade. Even small practices have faced significant penalties for failing to complete a documented HIPAA risk assessment.
Darkhorse Tech has created this guide to help dental professionals understand what a HIPAA risk assessment involves, how to perform one properly, and what mistakes to avoid.

Understanding HIPAA Compliance in Dental Settings
HIPAA compliance means more than having a privacy policy or secure email. It involves meeting three key regulatory standards established by HHS:
1. The Privacy Rule
Defines how patient information can be used and disclosed.
2. The Security Rule
Specifies the safeguards required to protect electronic patient data, including technical, administrative, and physical measures.
3. The Breach Notification Rule
Outlines the process for notifying patients and regulators in the event of a data breach.
The Security Rule is where the HIPAA risk assessment requirement lives. Every covered entity, including dental practices and dental service organizations (DSOs), must conduct a risk analysis to evaluate the potential risks and vulnerabilities to the confidentiality, integrity, and availability of ePHI.
What a HIPAA Risk Assessment Actually Is
A HIPAA risk assessment is a structured review of your systems, policies, and workflows to identify where patient information could be exposed. It looks at both technical and human factors that could lead to unauthorized access, loss, or disclosure of data.
According to the OCR, a compliant risk assessment must:
- Identify where all ePHI is created, received, maintained, or transmitted
- Assess the likelihood and impact of potential threats
- Determine existing security measures and their effectiveness
- Identify gaps or vulnerabilities
- Document findings, risk levels, and mitigation actions
Think of it as a detailed map of your data environment and a scorecard of how well you are protecting it.
The Three Domains of HIPAA Safeguards

Administrative Safeguards
Policies, procedures, and training that govern who can access ePHI and how. Examples include role-based access, workforce training, and vendor management.
Technical Safeguards
Technology controls such as encryption, access logging, secure email, multi-factor authentication, and automatic session timeouts.
Physical Safeguards
Physical measures that protect systems and devices. Examples include locked server rooms, secure disposal of drives, and restricted workstation access.
Each domain plays a vital role in reducing risk. If one fails, the others cannot fully compensate. For a deeper breakdown of common compliance gaps, see Darkhorse Tech's article on Why HIPAA Compliance is Non-Negotiable for Dental Offices.
The Step-by-Step HIPAA Risk Assessment Process
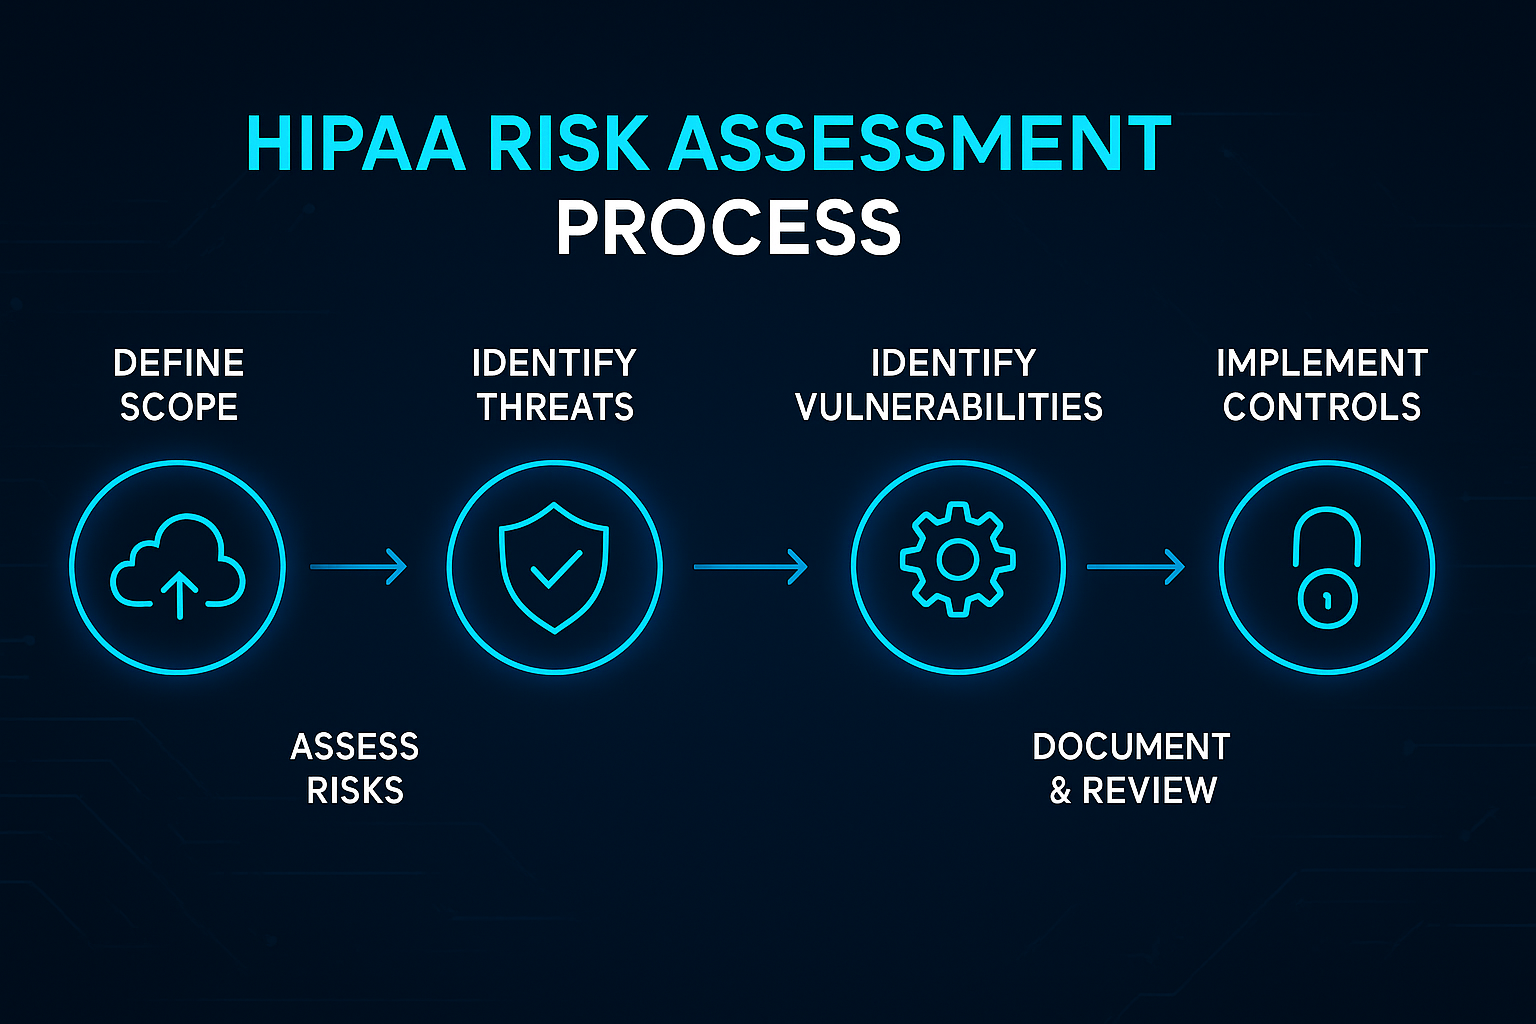
- 1Define the ScopeList all systems, networks, software, and devices that store or access ePHI — imaging systems, practice management software like Open Dental or Dentrix, email servers, mobile devices, and backup drives.
- 2Identify ThreatsConsider potential risks such as ransomware, phishing, unauthorized access, hardware failure, or natural disasters.
- 3Identify VulnerabilitiesEvaluate where your systems or people might fail — shared logins, outdated software, missing patches, or lack of encryption.
- 4Assess Likelihood and ImpactRate how likely each threat is to occur and how damaging it would be. Combine these factors to calculate a risk score.
- 5Determine Controls and Mitigation StepsDocument what safeguards exist and what improvements are needed, such as enabling encryption on backups or training staff to recognize phishing emails.
- 6Document and ReviewKeep a written record of all findings and mitigation plans. The OCR expects documentation that demonstrates ongoing risk management, not a one-time checklist.
Darkhorse Tech recommends performing a full review annually and updating it after any major system change, such as migrating to the cloud or switching practice management software.
Common Pitfalls and Audit Red Flags
Through years of dental IT compliance work, Darkhorse Tech has identified recurring mistakes that trigger OCR findings or increase breach risk.
- Believing the IT provider handles compliance entirely
- Lack of signed Business Associate Agreements (BAAs) with vendors
- No ongoing HIPAA training for staff
- Risk assessments performed but not documented
- Using general MSPs with no dental or HIPAA specialization
- Storing backups or patient data on unencrypted drives
- Outdated antivirus or unsupported operating systems
For clarity on how audits differ from assessments, see HIPAA Security Rule Updates: What Dental Practices Need to Know.
The Dental HIPAA Risk Assessment Checklist (2025/2026 Edition)
To help practices start correctly, Darkhorse Tech offers a downloadable Dental HIPAA Risk Assessment Checklist. The checklist outlines the key administrative, technical, and physical controls required by HIPAA. Sections include:
- Administrative Safeguards: policy documentation, training, vendor management
- Technical Safeguards: access controls, encryption, data transmission, backups
- Physical Safeguards: facility access, workstation security, media disposal
- Documentation Tracker: a space to log your current compliance status and next actions
You can download the full checklist in PDF format from the Darkhorse Tech website. It serves as both a learning tool and a quick reference during internal audits.
How Darkhorse Tech Conducts HIPAA Risk Assessments
Darkhorse Tech provides end-to-end HIPAA risk assessment services designed specifically for dental organizations. Our approach combines automated scanning tools, deep knowledge of dental practice software, and hands-on analysis from compliance specialists. Our process includes:
- Full inventory of all systems containing ePHI
- Automated vulnerability scanning and penetration testing
- Interviews with key staff to evaluate administrative controls
- Risk scoring and prioritized mitigation roadmap
- Delivery of a complete report and documentation for OCR readiness
Read more about their work here. Darkhorse Tech's focus on the dental industry allows us to anticipate challenges unique to dental IT environments, including imaging integration, Open Dental Cloud migrations, and multi-location networks.
Next Steps
Performing a HIPAA risk assessment is not just a compliance task; it is a business safeguard. It reduces your exposure to data breaches, builds patient trust, and ensures operational continuity if incidents occur.
Darkhorse Tech helps dental practices across the United States meet HIPAA requirements with confidence. Our specialists combine compliance expertise with hands-on IT management to make the process practical, repeatable, and stress-free.
Read our best tips for ensuring cybersecurity and HIPAA compliance for your dental practice.
Schedule a complimentary compliance consultation.
Darkhorse Tech is here to review your current HIPAA readiness and provide a sample mitigation plan.

